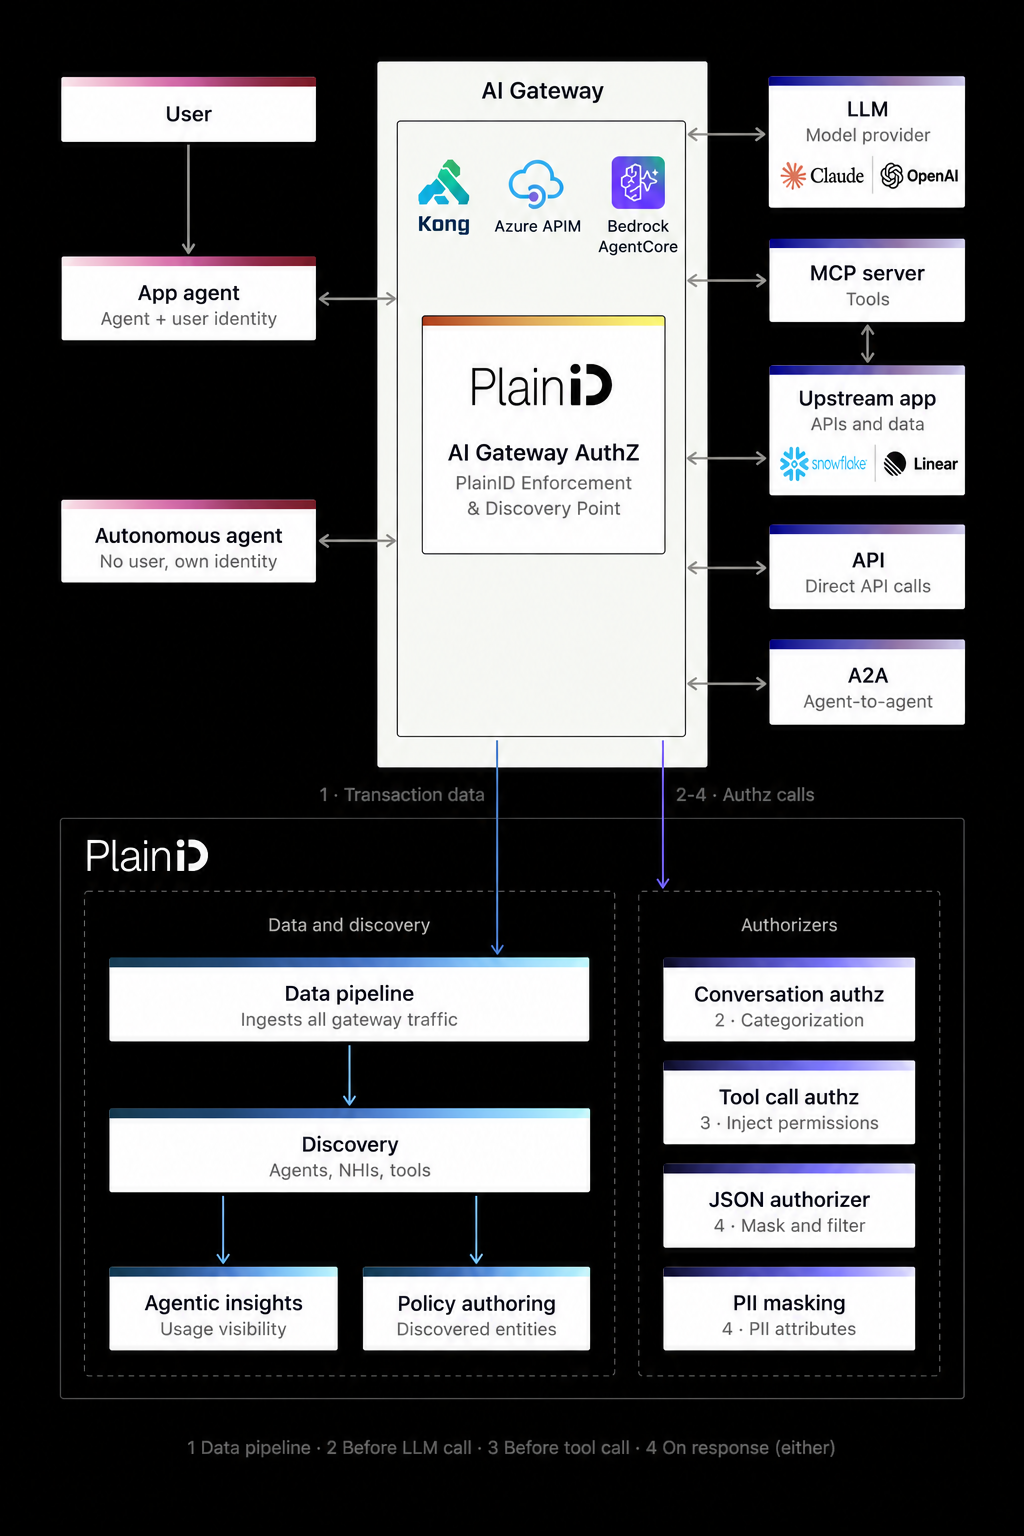
AI agents often reach enterprise APIs and Model Context Protocol (MCP) tools through a gateway. This makes the gateway a natural control point for authorization, and a natural vantage point for seeing what agents actually do.
PlainID integrates smoothly with leading gateways through dedicated Authorizers. Each Authorizer plugs into the gateway you already run, with minimal configuration. You don't need to modify your agents, MCP servers, or upstream services, or reroute any traffic.
Each Authorizer serves two roles:
- Enforcement: The Authorizer acts as a Policy Enforcement Point (PEP). It sends the identity and request context to the PlainID Policy Decision Point (PDP) and enforces the decision before the request reaches the upstream service.
- Discovery and insights: The gateway serves as an interception point for agentic activity. As agents call APIs and MCP tools, PlainID discovers the agents and tools in use and creates them in the Platform. You can then use them to author Policies and to gain insights into how agents access your resources.
You manage Policies centrally in the Platform, and a Policy change takes effect on the next call, with no changes to agents or upstream services.
PlainID currently supports the following API, AI, and MCP gateways:
- Kong Gateway: a single plugin enforces Policies on both MCP tool calls and REST API calls. For MCP servers, it filters which tools each agent can see and use. For permitted calls, it can also mask sensitive response fields based on the initiating identity. See Kong Gateway.
- Azure API Management (APIM): applies fine-grained, Policy-based access control to APIs exposed through APIM. The Authorizer evaluates each request in real time based on identity, roles, and request context, and then permits or denies it. See Azure API Management Authorizer.
- Google Apigee: brings PlainID Policies to the APIs you publish through Apigee. For each incoming request, the Authorizer checks the identity, roles, and request context with the PDP and enforces the permit or deny decision before the request reaches the upstream service. See Apigee Authorizer{target=_blank}.
- Amazon Bedrock AgentCore: extends PlainID runtime authorization to agents built and deployed on Amazon Bedrock AgentCore. The Authorizer evaluates the tool and API calls that agents make through AgentCore Gateway, and PlainID discovers the agents and tools in use. See Amazon Bedrock AgentCore Authorizer.
- Microsoft Foundry: extends PlainID runtime authorization to agents built and deployed on Microsoft Foundry. The Authorizer evaluates the tool and API calls that Foundry agents make, and PlainID discovers the agents and tools in use. See Microsoft Foundry Authorizer.