The PlainID integration for Kong Gateway enforces PlainID Policies directly at your gateway. You can govern REST APIs, MCP servers, and LLM traffic under the same Policies you already manage in PlainID, without changing your upstream services.
The integration runs as a set of Kong plugins on your own Kong data plane. You install the plugins once, then attach them to the routes you want to protect. Kong handles the traffic and the plugin configuration, and PlainID evaluates each transaction against your Policies in real time. When you change a Policy, the change applies on the next request, with no redeploy and no Kong configuration change.
The PlainID Plugins
PlainID provides four plugins. Three of them enforce Policies, one for each kind of route. The fourth sends transactional data to PlainID and runs alongside any of the others.
| Plugin | Attach it to | What it does |
|---|---|---|
plainid-api-authz |
REST API routes | Asks PlainID to permit or deny each request. Kong blocks denied requests before they reach your API. |
plainid-mcp-authz |
MCP server routes | Filters the tool list so each caller sees only the tools its Policies allow, and authorizes every tool call. It can also report each MCP server's tool inventory to PlainID for discovery. |
plainid-prompt-authz |
LLM routes served by Kong AI Gateway | Applies Prompt Control to the input: checks which content categories the prompt touches and blocks prompts the caller may not send. Applies Output Control to the output: masks or encrypts sensitive data in the model's response before it reaches the caller. |
plainid-insights |
Any route | Sends transactional data for each inbound request to the PlainID Collector, which PlainID uses for agentic insights. It never blocks or changes a request. |
How It Works
For each request on a protected route:
- A Kong authentication plugin, such as
openid-connectorjwt, identifies the caller. - The PlainID plugin sends the caller's identity and the request details to the PlainID Policy Decision Point (PDP).
- The PDP evaluates your Policies and returns a decision.
- The plugin forwards permitted requests to the upstream service and blocks denied ones. For LLM routes, the plugin can also mask the model's response on the way back.
If a plugin cannot reach PlainID, or cannot verify what it would forward, it denies the request instead of letting it through.
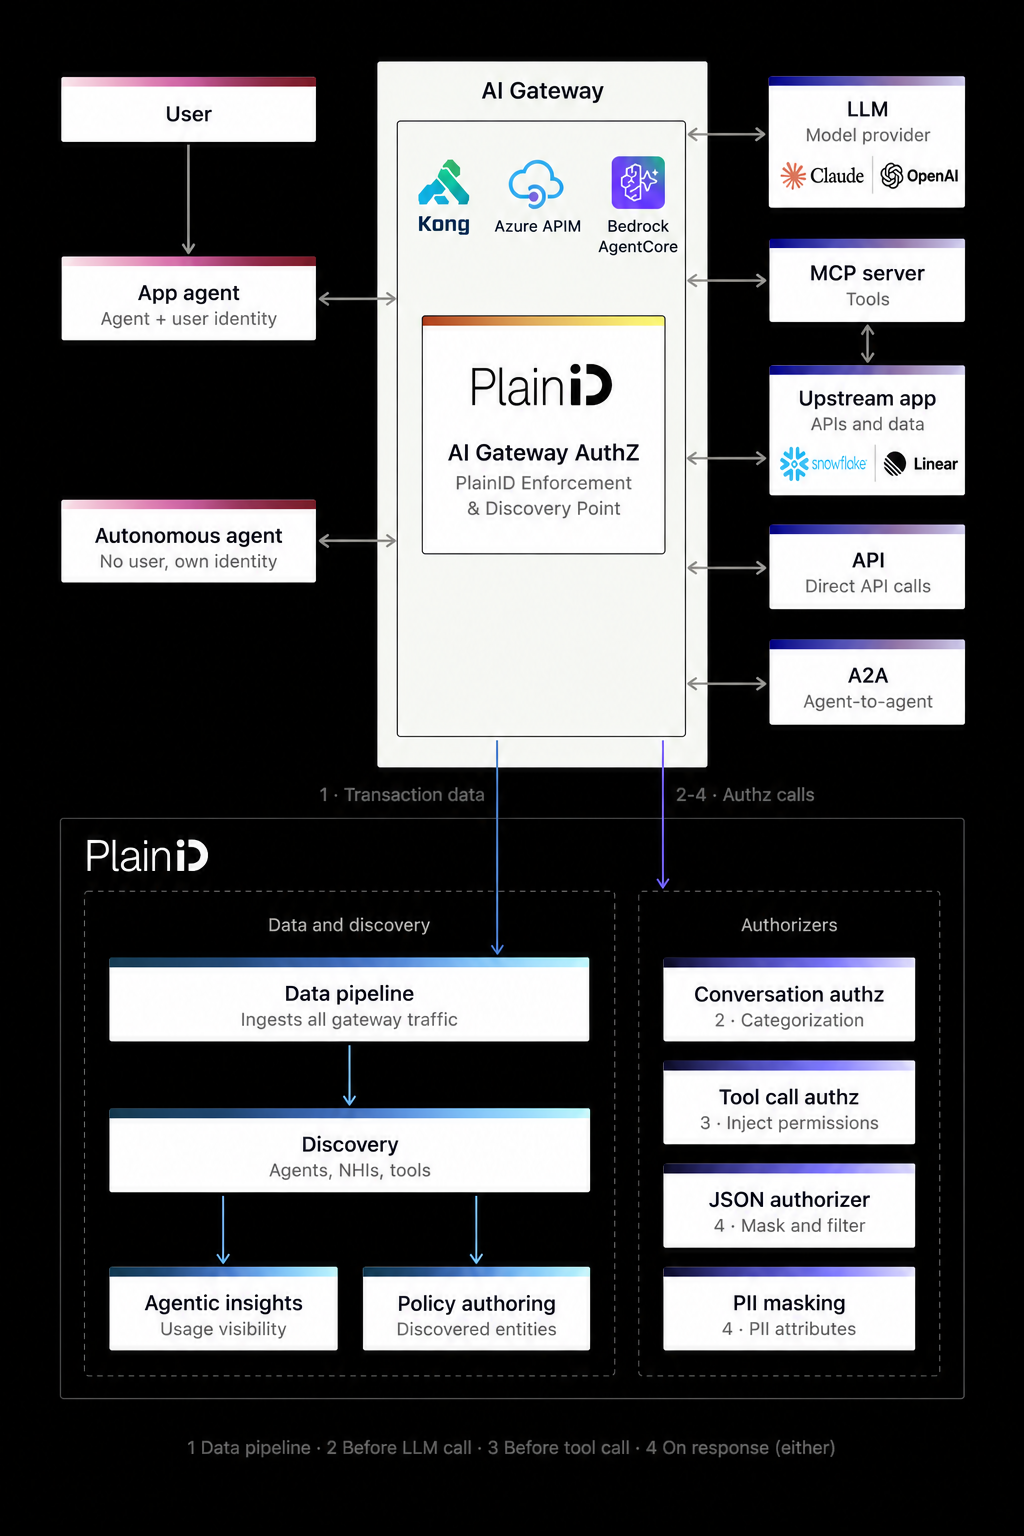
Each Kong route serves exactly one kind of traffic: a REST API, an MCP server, or an LLM endpoint. Attach exactly one enforcement plugin to each route: plainid-api-authz, plainid-mcp-authz, or plainid-prompt-authz. Each plugin reads the request body in its own format, so two enforcement plugins on the same route misread each other's traffic. PlainID does not support this configuration.
plainid-insights is the exception. You can attach it to any route alongside one of the enforcement plugins.
Supported Deployments
The plugins run on self-managed Kong Gateway data planes, including on-premises deployments and data planes connected to a Kong Konnect control plane.
MCP tool discovery and plainid-insights require a data plane connected to a Konnect control plane. On a data plane without Konnect, plainid-api-authz, plainid-mcp-authz, and plainid-prompt-authz still enforce Policies, but PlainID receives no tool inventories and no transactional data.
See Configuring Kong to install the plugins and configure them on your routes.