The PlainID Azure API Management Authorizer enforces PlainID Policies on the REST APIs and MCP servers you expose through Azure API Management (APIM), without changing your backend services. The Authorizer ships as a set of APIM policy fragments. You add the fragments you need to each API operation, and APIM consults PlainID's Policy Decision Point (PDP) at request time.
The Authorizer provides five capabilities:
- API authorization: for each REST call, the PDP decides whether to permit or deny the request. APIM blocks denied calls before they reach the backend service.
- MCP tool governance: for MCP servers, the Authorizer filters the tool list each identity receives and authorizes every tool call, so an Agent sees and uses only the tools its Policies allow.
- MCP discovery: the Authorizer registers the full tool inventory of each MCP server with PlainID. You use this inventory when you author Policies.
- Agent discovery: the Platform discovers the Agents that work through your APIM instance, so you can see which Agents call your APIs and MCP servers and govern them with Policies.
- Insights: the Authorizer intercepts the transactions that pass through APIM and reports them to the Platform, giving you visibility into the traffic between Agents, clients, APIs, and MCP servers.
MCP discovery, Agent discovery, and Insights report to an Azure APIM POP in the Integrations Workspace, where you can review the MCP servers, tools, and Agents the Platform discovers. See Configuring the Azure API Management Authorizer for more information.
All decisions draw on the Policies you already manage in PlainID. PlainID evaluates each request in real time, so a Policy change takes effect on the next call. No redeploy or APIM configuration change required.
How It Works
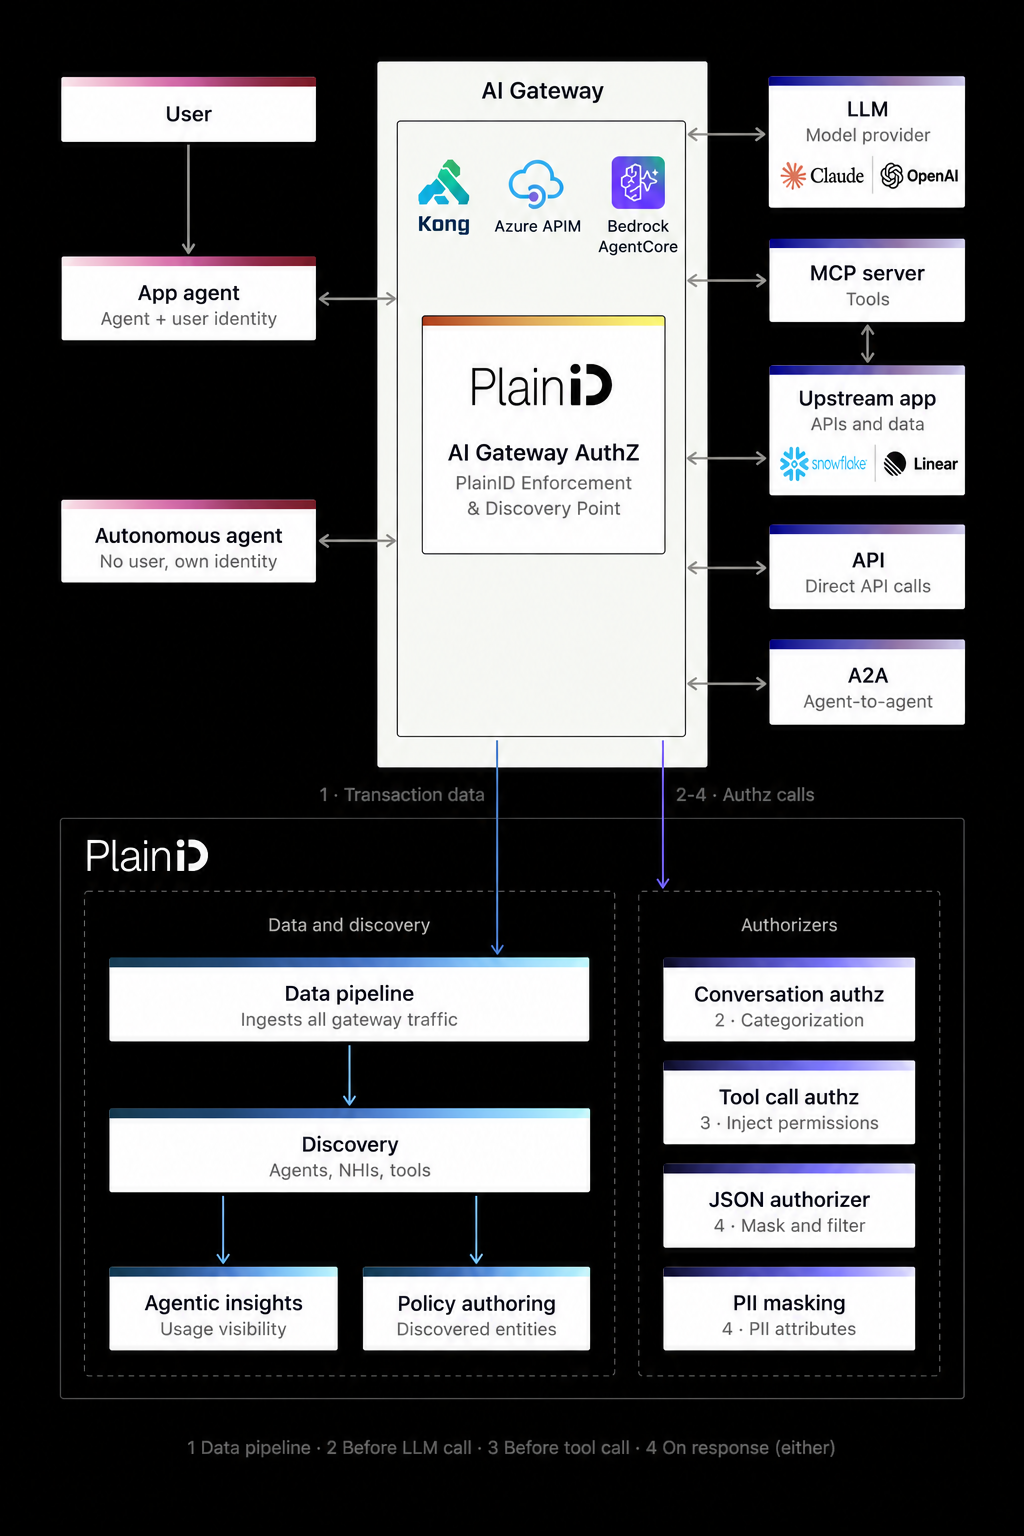
REST API Requests
- An application or Agent calls an API exposed through APIM. If you enabled Insights, the Authorizer reports the request to PlainID.
- The Authorizer builds an authorization request from the call's identity, headers, path, query parameters, and body, and sends it to the PDP.
- The PDP evaluates your Policies and returns a Permit or Deny decision.
- On Permit, APIM forwards the request to the backend service and returns the backend's response to the caller. On Deny, APIM returns your configured deny response, and the request never reaches the backend.
MCP Requests
- An Agent asks the MCP server for its tools (
tools/list). If you enabled Insights, the Authorizer reports the request to PlainID. APIM forwards the request to the MCP server. - On the way back, the Authorizer registers the complete tool list with PlainID, then asks PlainID which tools this identity may use and removes the rest from the response.
- The Agent calls a tool (
tools/call). Before the call reaches the MCP server, the Authorizer sends the tool name and arguments to the PDP. - On Permit, APIM forwards the call to the MCP server. On Deny, APIM returns a JSON-RPC error to the Agent, and the call never reaches the MCP server.
See Configuring the Azure API Management Authorizer for installation and configuration steps.