The Amazon Bedrock AgentCore Gateway Authorizer enforces PlainID Policies on the Model Context Protocol (MCP) tools your AI agents reach through an Amazon Bedrock AgentCore Gateway, without changing your gateway targets. The Authorizer ships as an AWS CloudFormation template and an AWS Lambda function. The gateway calls the function as an interceptor on every MCP request and response, and the function consults PlainID's Policy Decision Point (PDP) at request time.
The Authorizer provides three capabilities:
- MCP tool governance: the Authorizer filters the tool list each identity receives, including semantic search results, and authorizes every tool call, so an agent sees and uses only the tools its Policies allow.
- MCP discovery: the Authorizer reports the full tool inventory of each gateway target to PlainID. You use this inventory when you author Policies.
- Agent dynamic discovery: the Authorizer identifies each AI agent that calls the gateway from the caller’s token and reports it to PlainID, so new agents appear in the Platform as they start making requests. You use these agent identities when you author Policies for specific user-agent combinations.
- Transactional reporting: the Authorizer reports each tool call that passes through the gateway to PlainID, including the caller's token, so PlainID can identify the calling agent.
MCP discovery and transactional reporting send records to the gateway's AWS Bedrock AgentCore Gateway POP in the Integrations Workspace, where you review the MCP servers, tools, and agents the Platform discovers. See POP Setup for more information.
How It Works
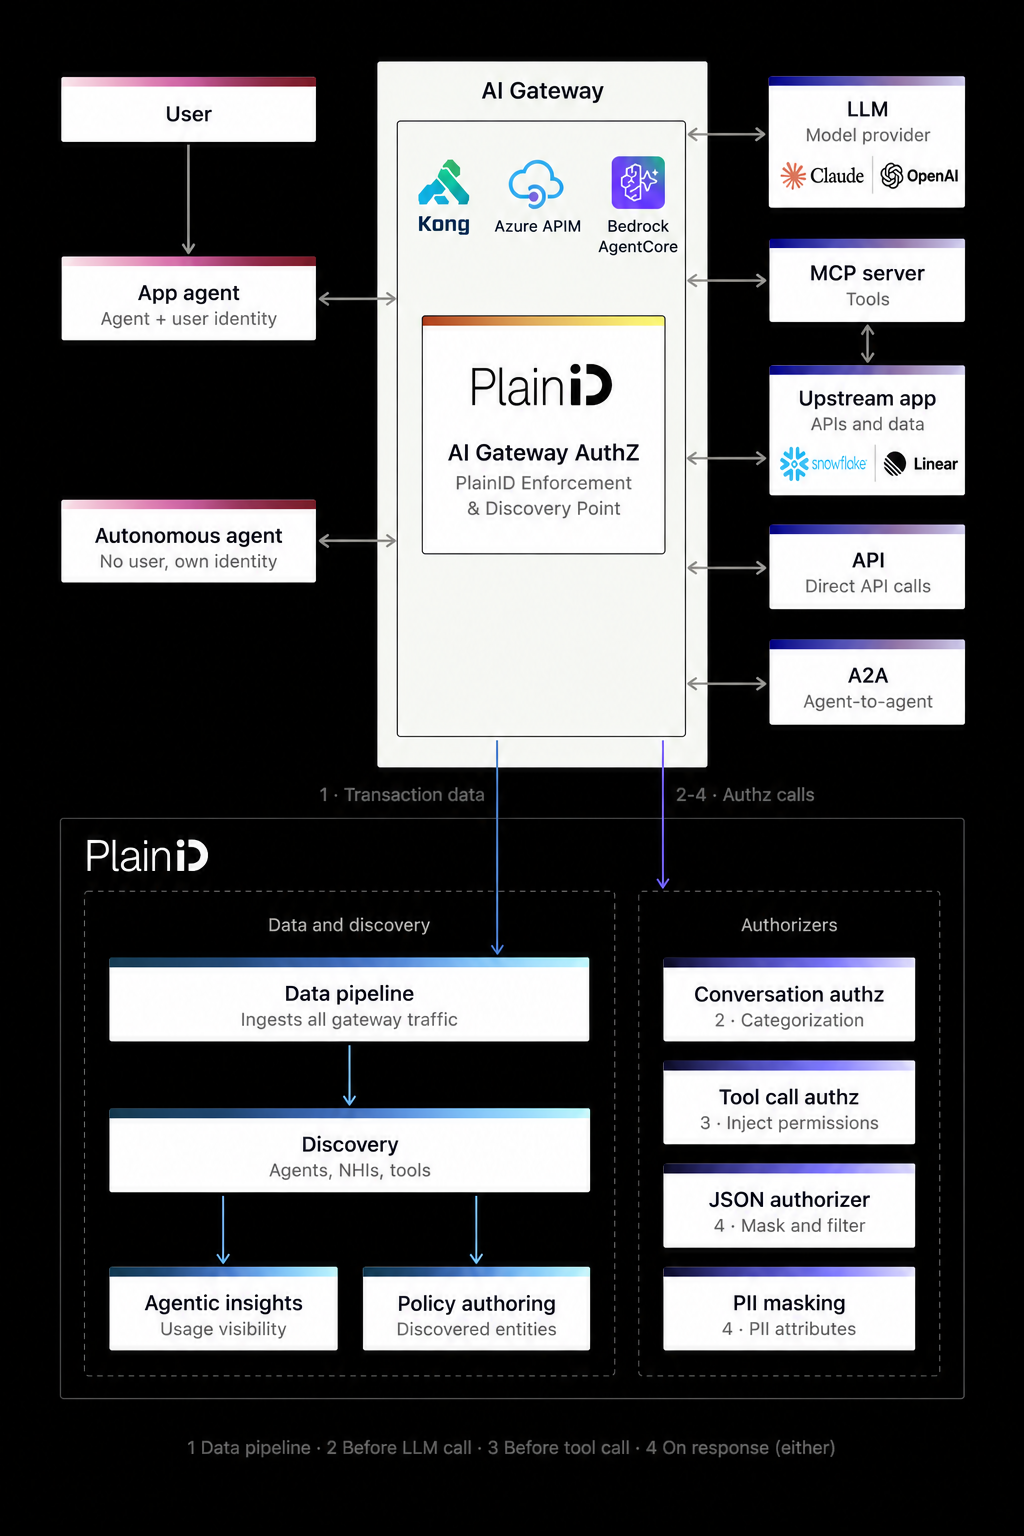
The Authorizer covers the MCP server path in this diagram: tool list filtering, tool call authorization, MCP discovery, and transactional reporting.
- An agent asks the gateway for its tools (tools/list), or runs a semantic search. The gateway collects the tools from its targets.
- On the way back, the Authorizer reports the complete tool list to PlainID if you enabled MCP discovery. It then asks the PDP which tools this identity may use and removes the rest from the response, on every page of the list.
- The agent calls a tool (tools/call). Before the call reaches the target, the Authorizer sends the tool name, the arguments, and the caller's token to the PDP. If you enabled transactional reporting, the Authorizer also reports the call to PlainID.
- On Permit, the gateway forwards the call to the target. On Deny, the gateway returns a JSON-RPC error to the agent, and the call never reaches the target.
When it can't reach the PDP, can't read a request, or can't load its configuration, it blocks the request and never returns an unfiltered tool list.
Reporting to PlainID never affects the authorization decision. The Authorizer computes its decision first and hands the reports to a queue, so a slow or unavailable PlainID collector never blocks or delays a request.
See Configuring the Amazon Bedrock AgentCore Gateway Authorizer for installation and configuration steps.